Longhorn PHP 2026 - Day 1 Notes
Scott Keck-Warren • October 18, 2026
I was lucky enough to be able to attend Longhorn PHP 2026 and these are my more or less raw notes from day 1.
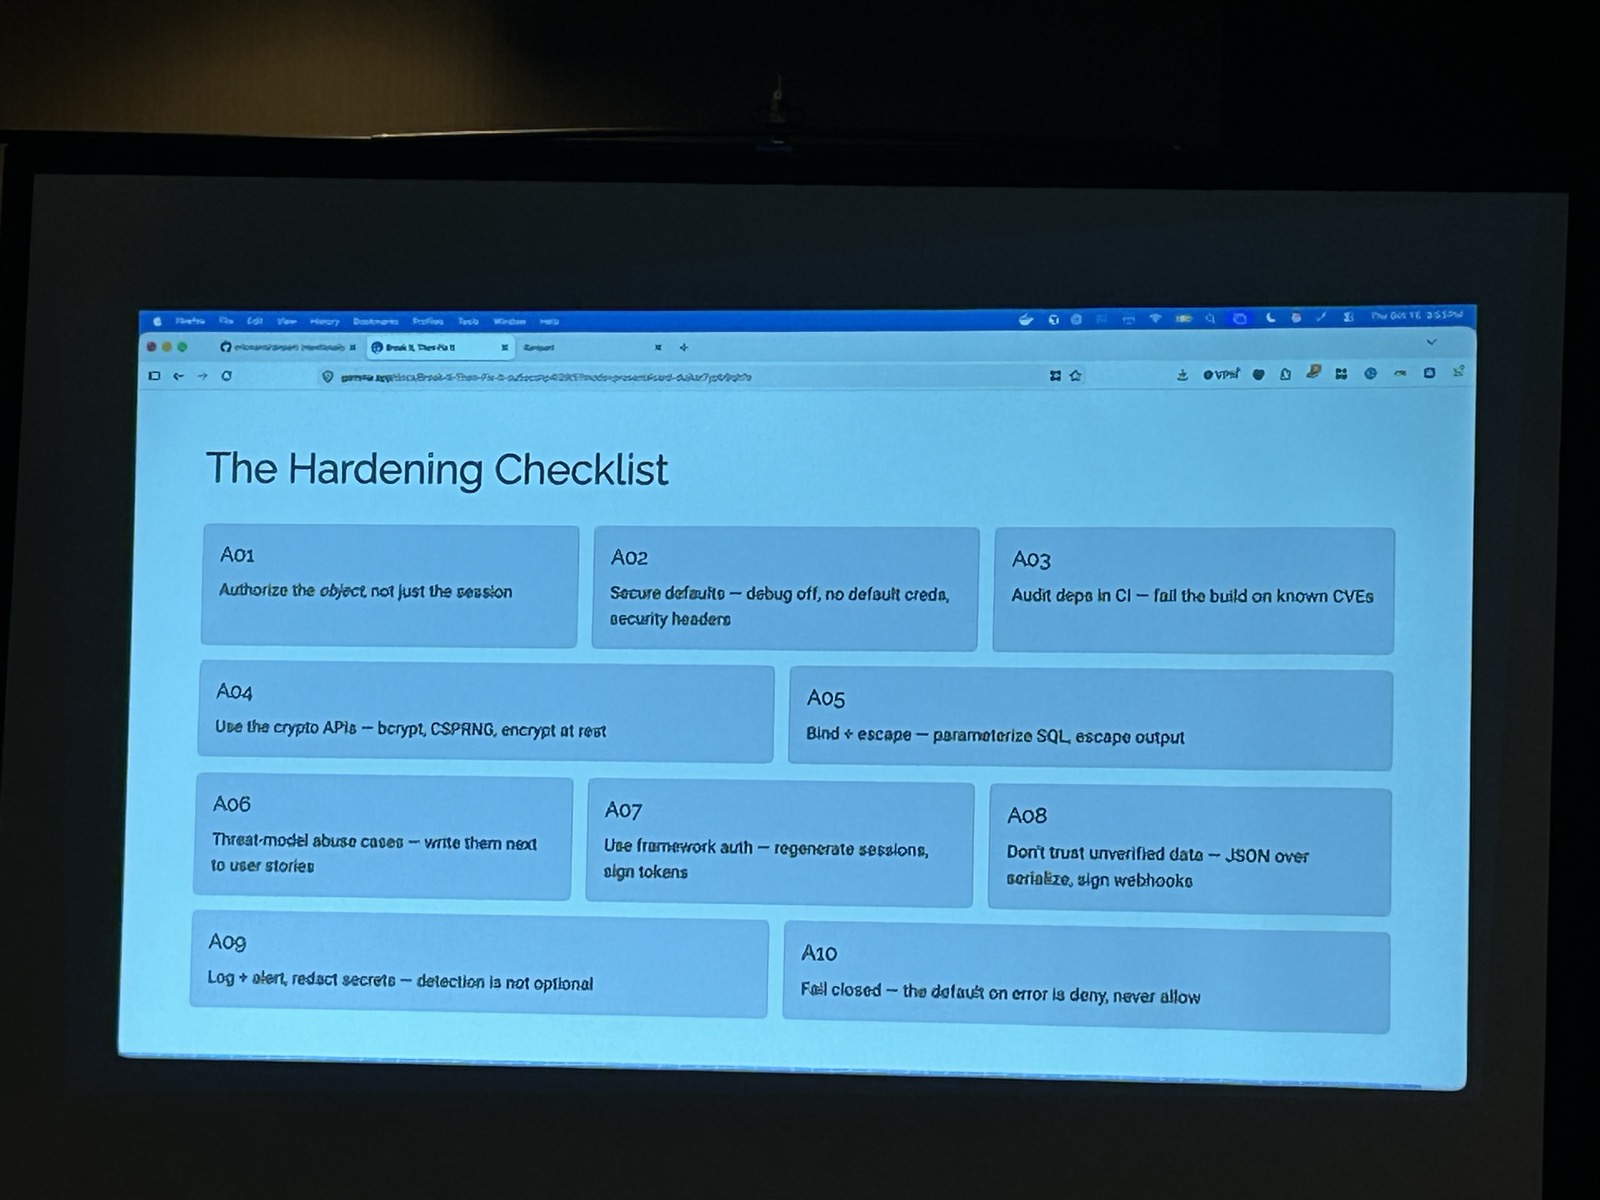
OWASP Top 10
- Threat Modeling in 90 Seconds
- What's the worst thing someone could make it do
- #1 Broken Access Control
- IDOR/BOLA - read anyones ticket by changing the ID
- Privilege Escalation - mass asign yourself role=admin
- NEVER trust the user
- Could change the
- SSRF
- http://metadata.internal is crazy
- #5 Injection
- SQL injection
- Use prepared statements
- HTML/JS injection
- Escape always
- Use Content-Security-Policy
- A07 Authentication Failures
- Session fixation
- Session ID doesn't reset
- Regenerate on every privilege change
- Forgeable "remember me" cookie
- Must be random, signed, and server-stored
- No MFA
- Use it
- Password reset token that don't expire
- They should
- A04 Cryptographic
- Using crypto incorrectly
- Use bcrypt or argon2
- Plaintext
- Encrypt API tokens at rest
- No TLS
- A02 Security Misconfiguration
- APP_DEBUG=true
- Default admin login
- Permission CORS
- Missing security headers
- Verbose errors exposed to end users
- A06 Insecure Design
- The flaw is the plan
- The core insight: the flaw is in the plan, not the code. You can't patch your way out of a bad design.
- Fixes
- Rate limiting
- Uniform responses
- Design-Time security
- A03 Software Supply Chain Failures
- Don't use tags in CI/CD and instead use SHA
- A08 Software or Data Integrity Failures
- Don't use serialize()/unserialize() use json_encode/json_decode
- Sign webhooks with HMAC
- A10 Mishandling of Exceptional C
- The failures the app doesn't prevent, doesn't detect, or responds badly to
- Classically, it fails open
- Fix
- Fail Closed
- Catch Narrowly
- Handle Deliberately
- Design for dependency failures
- A09 Security Logging and Alerting Failures
- Need to log successes and failures
- Always log in between 9 and 5 local time in Texas
- Problems
- Fix
- Log security events
- Alert on what matters
- Redact & protect